Assessment discipline
Criteria, review period, populations, sample selection and documented limits.
ATLANT SECURITY / SAMPLE AUDIT REPORT
Inspect the assessment.
Follow the conclusion.
A 32-page cybersecurity audit for fictional Asterion Group AG. See how procedures, sampled records and operating evidence become findings your management team can act on.
32 pages · Searchable PDF · By Atlant Security
Fictional organisation and assessment; not client work.
A REPORT YOU CAN INTERROGATE
Read the population and sample selection. Inspect the procedures and sanitised records. Follow each finding from the observed condition to the recommended action and the evidence needed for closure.
Every organisation, record and result in this report is invented for illustration. It demonstrates reporting technique, not a completed client engagement, certification or statutory audit opinion.
INSIDE THE ASSESSMENT
Scroll through selected pages, then request
the complete report below.
An original fictional cybersecurity control audit. The organisation, evidence and observations are invented; no real client assessment is claimed.
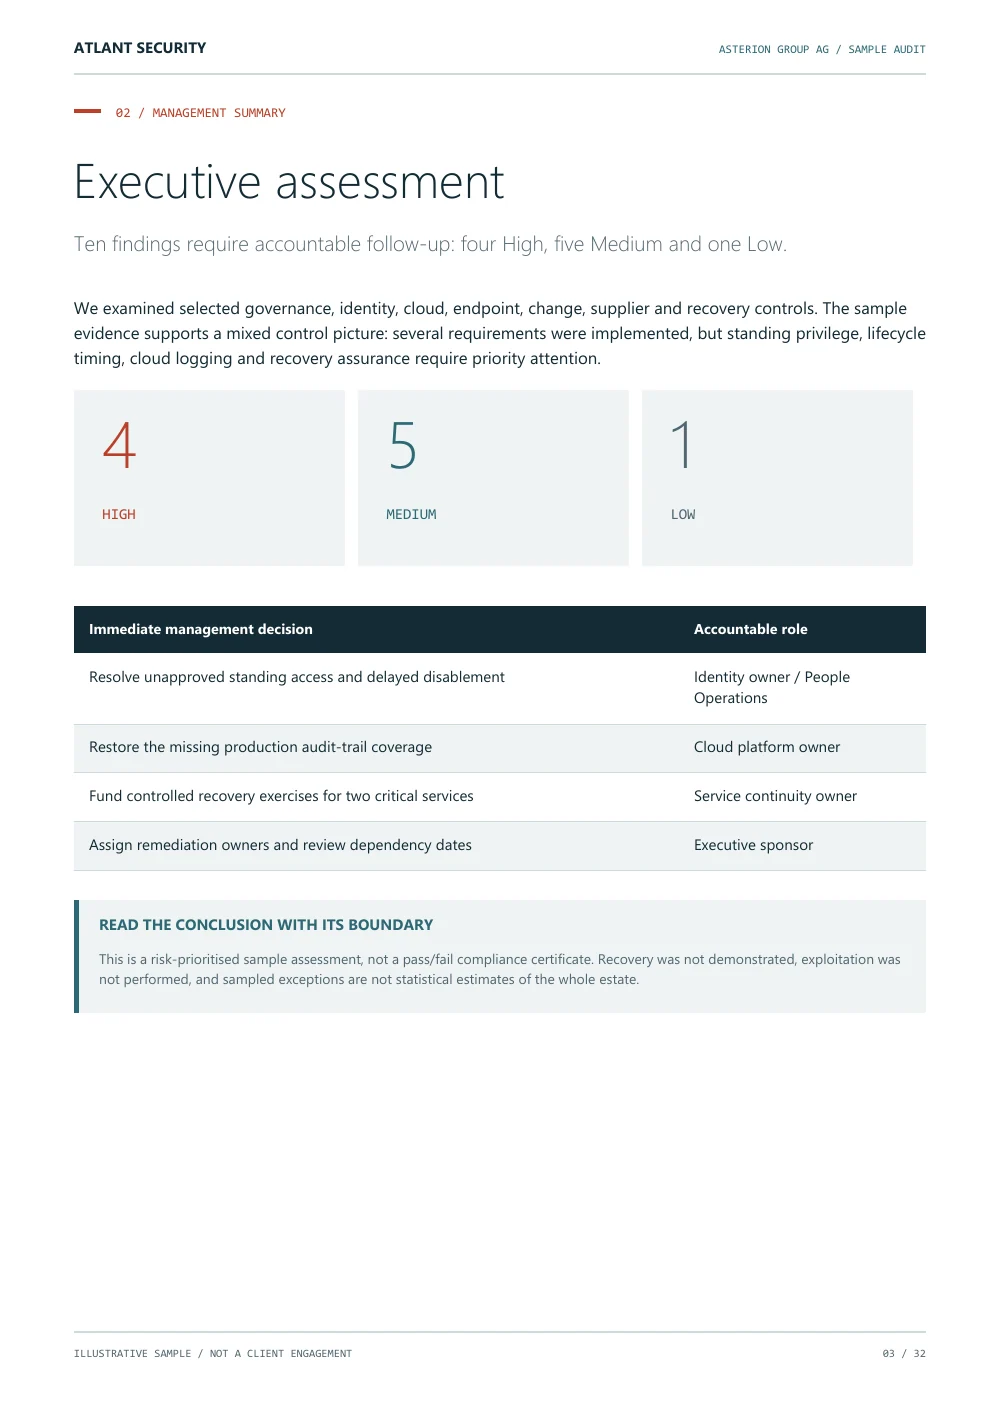
Ten findings: four High, five Medium and one Low. Priorities cover standing privilege, account disablement, cloud logging and recovery assurance.
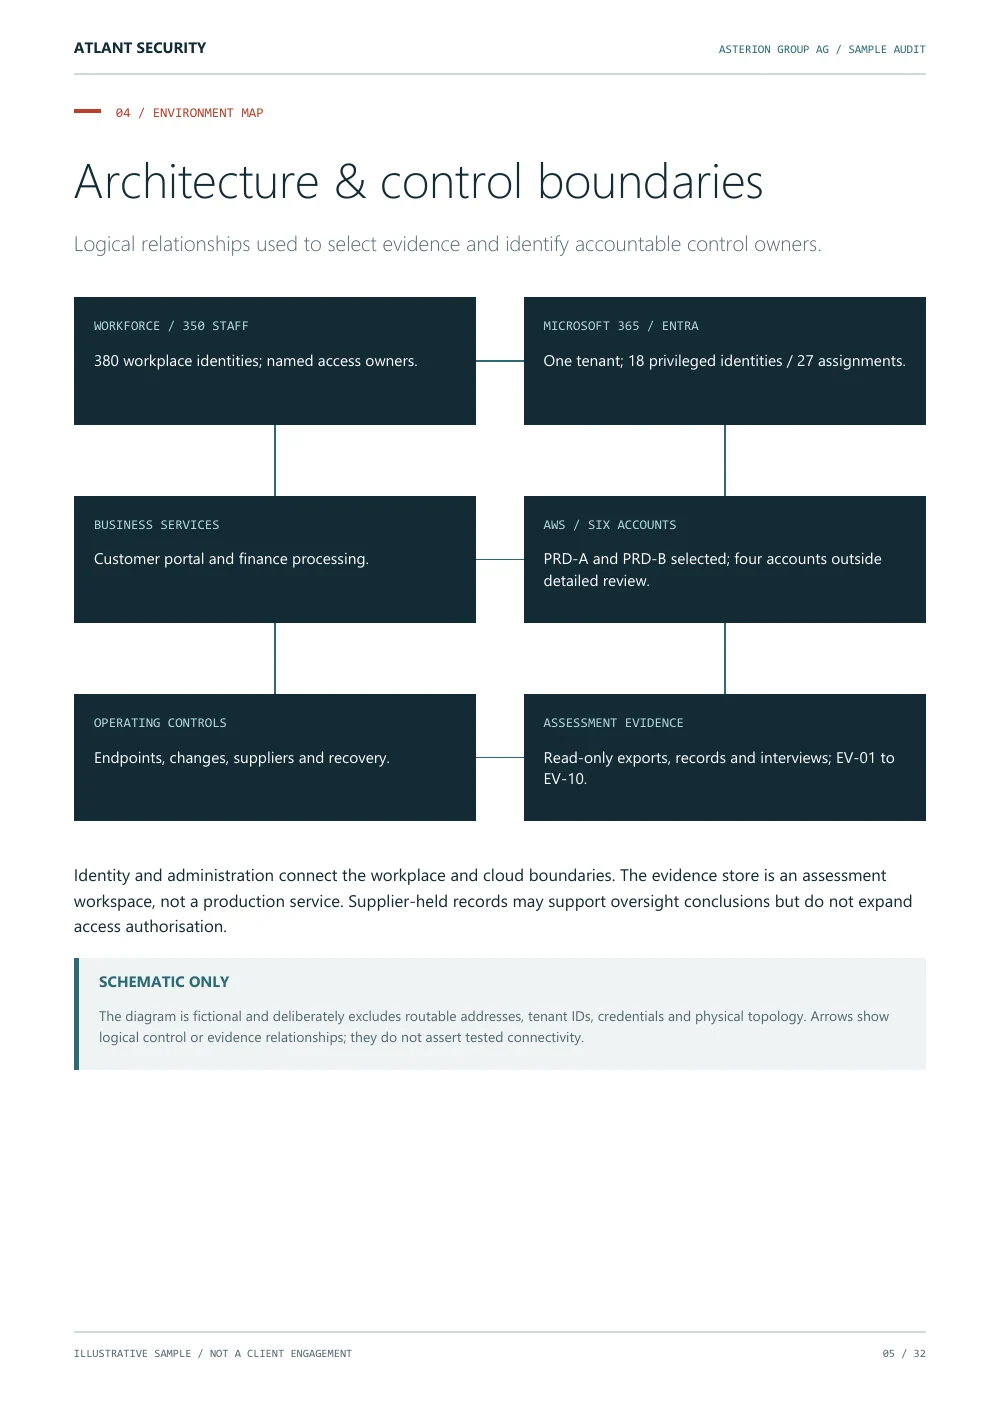
A logical map of the workplace, identity, AWS accounts, critical business services and the assessment evidence boundary.
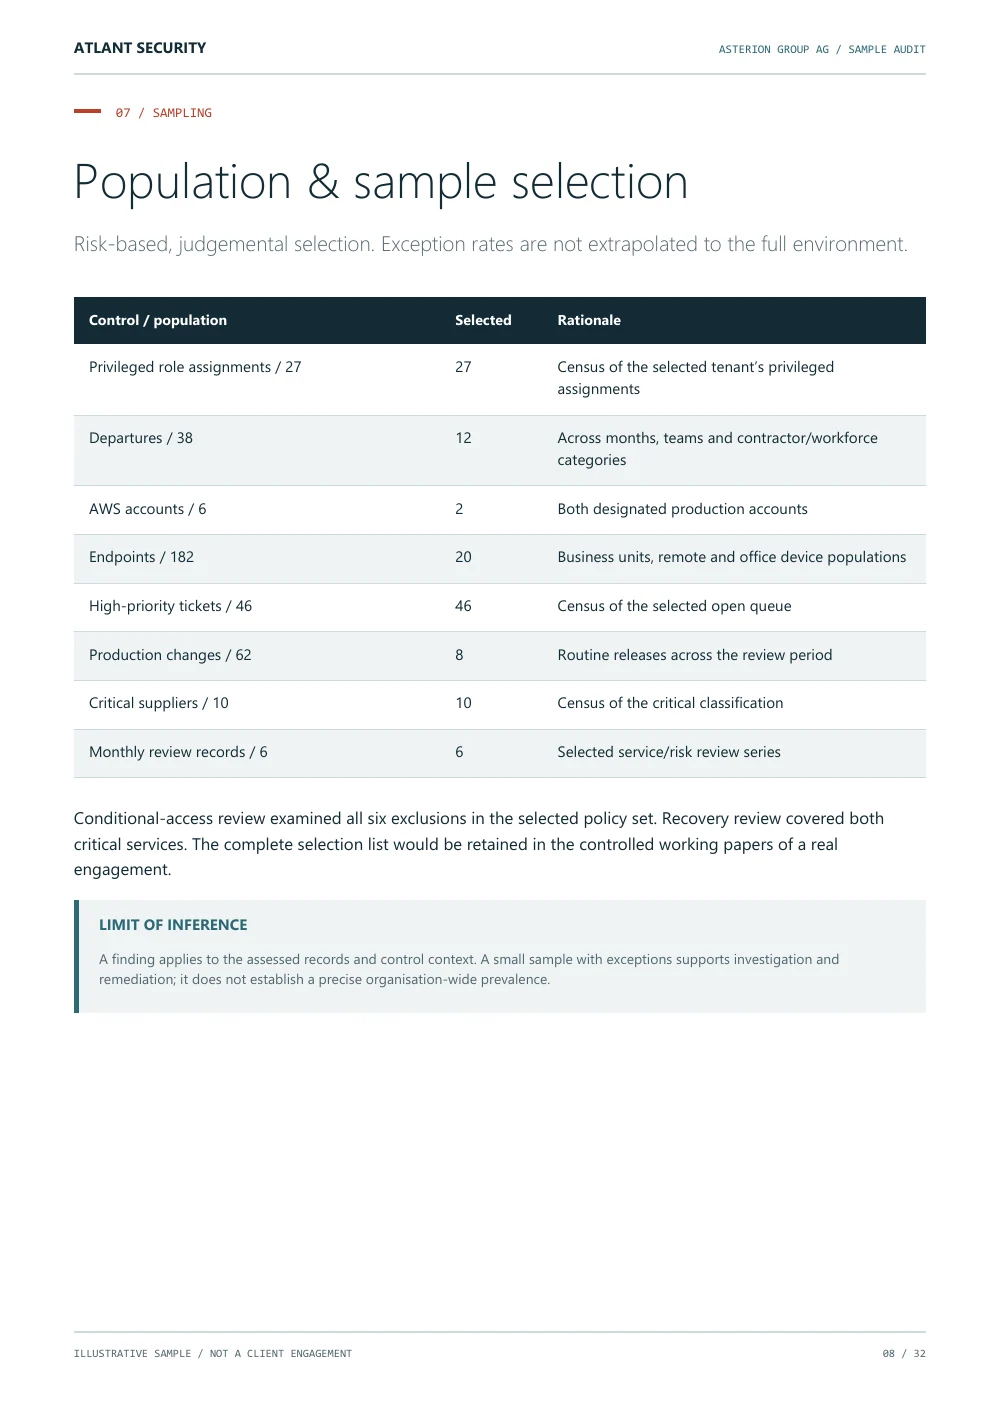
Selected populations include 27 role assignments, 12 of 38 departures, two of six cloud accounts and eight of 62 production changes. Judgemental samples are not extrapolated statistically.
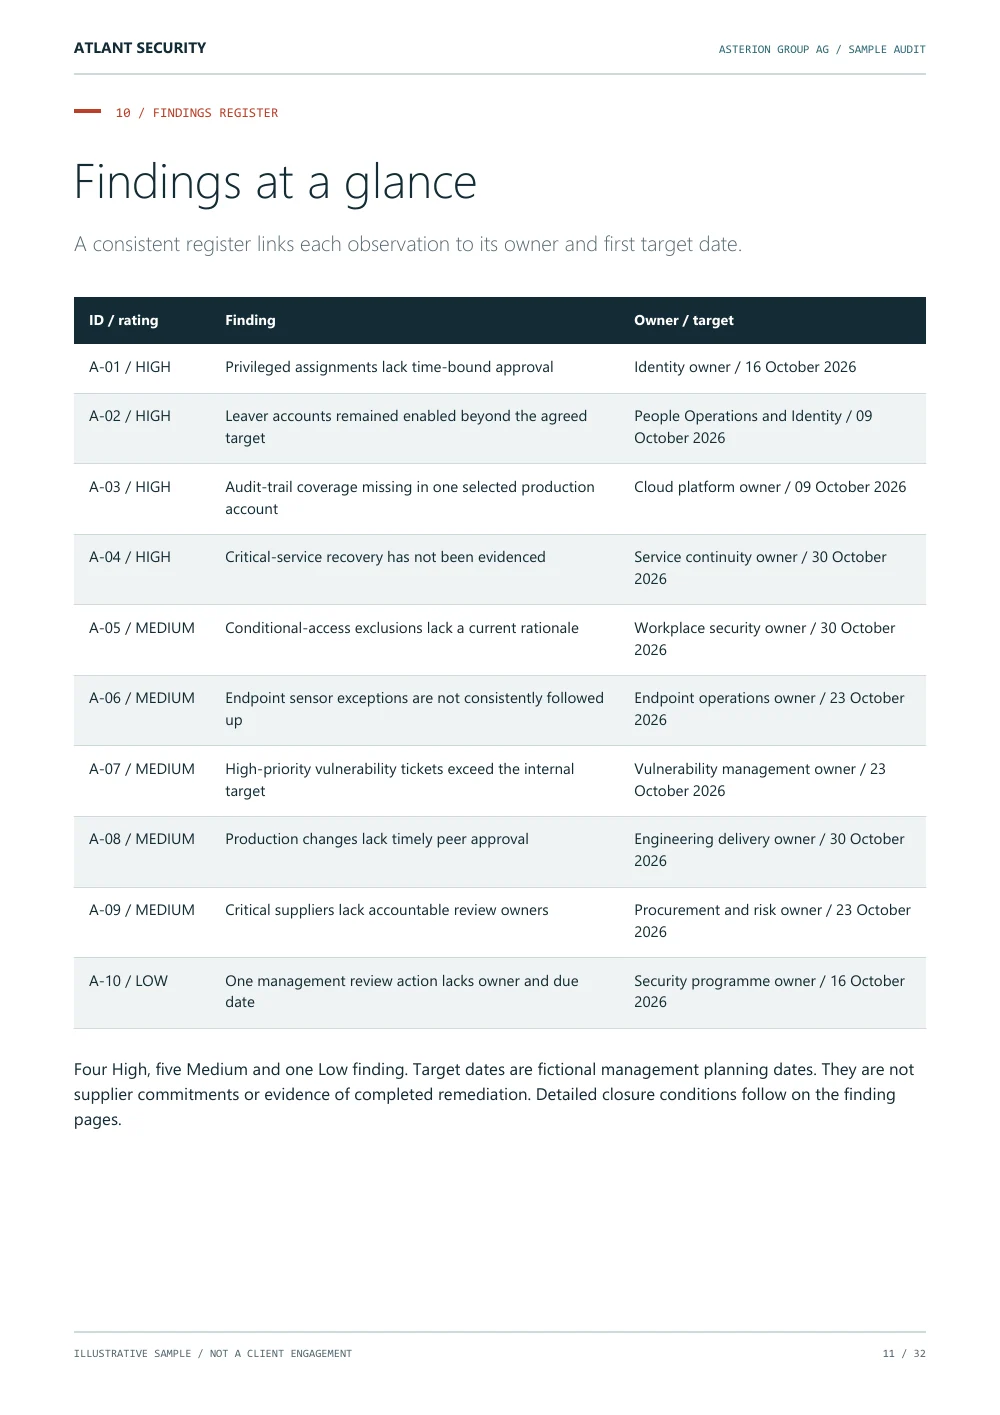
The findings register connects each issue to its severity, accountable owner and fictional management target date.
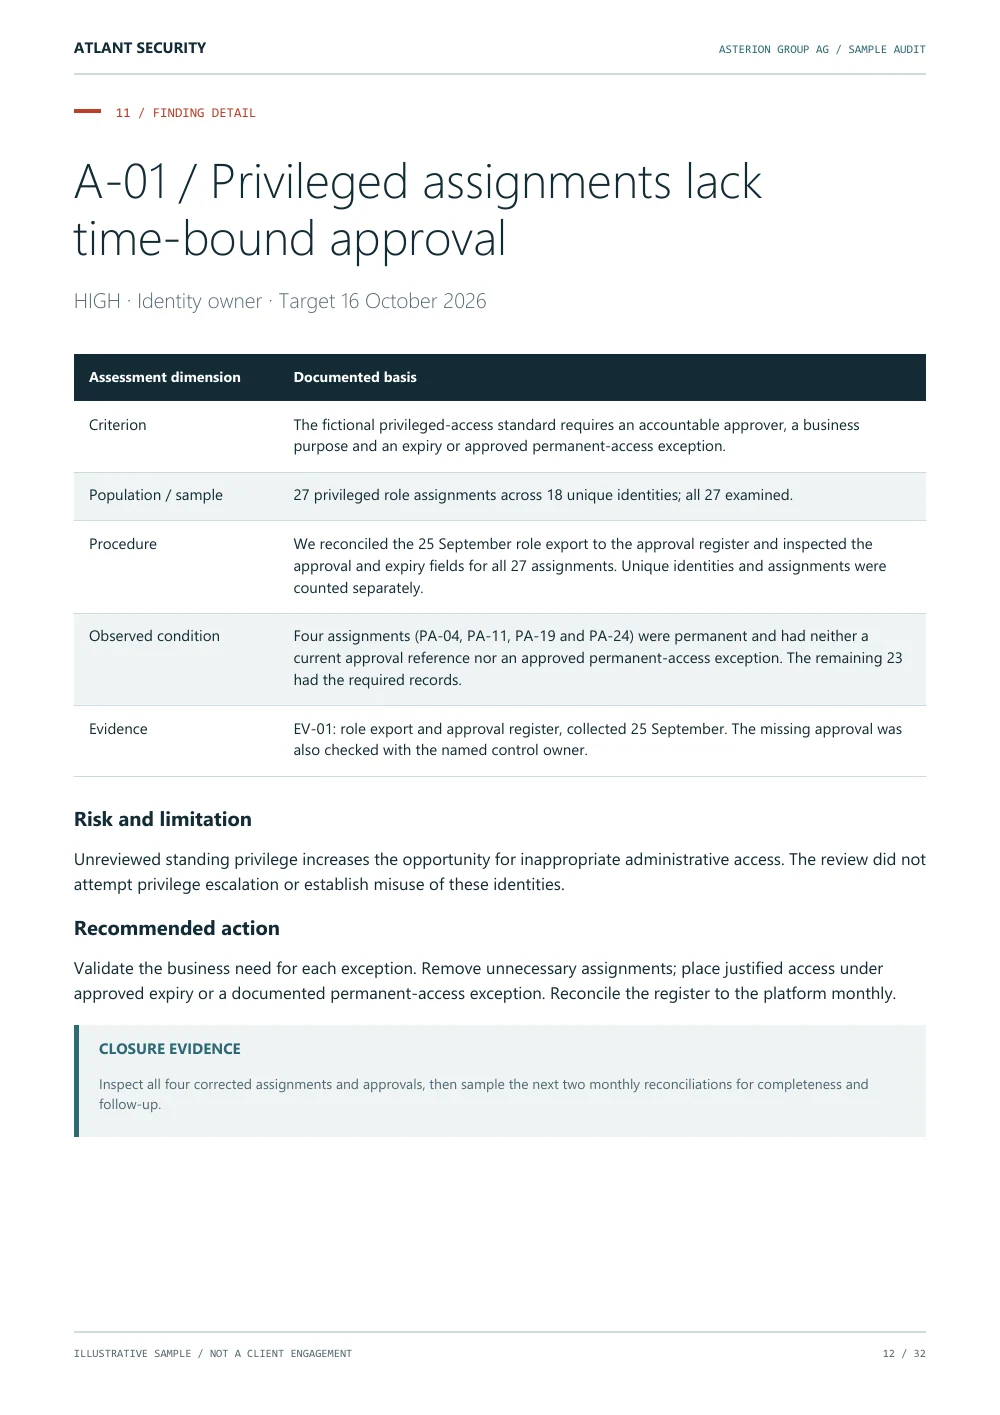
A-01 traces four assignments without current approval or an approved permanent-access exception to the criterion, procedure, risk, recommendation and closure conditions.
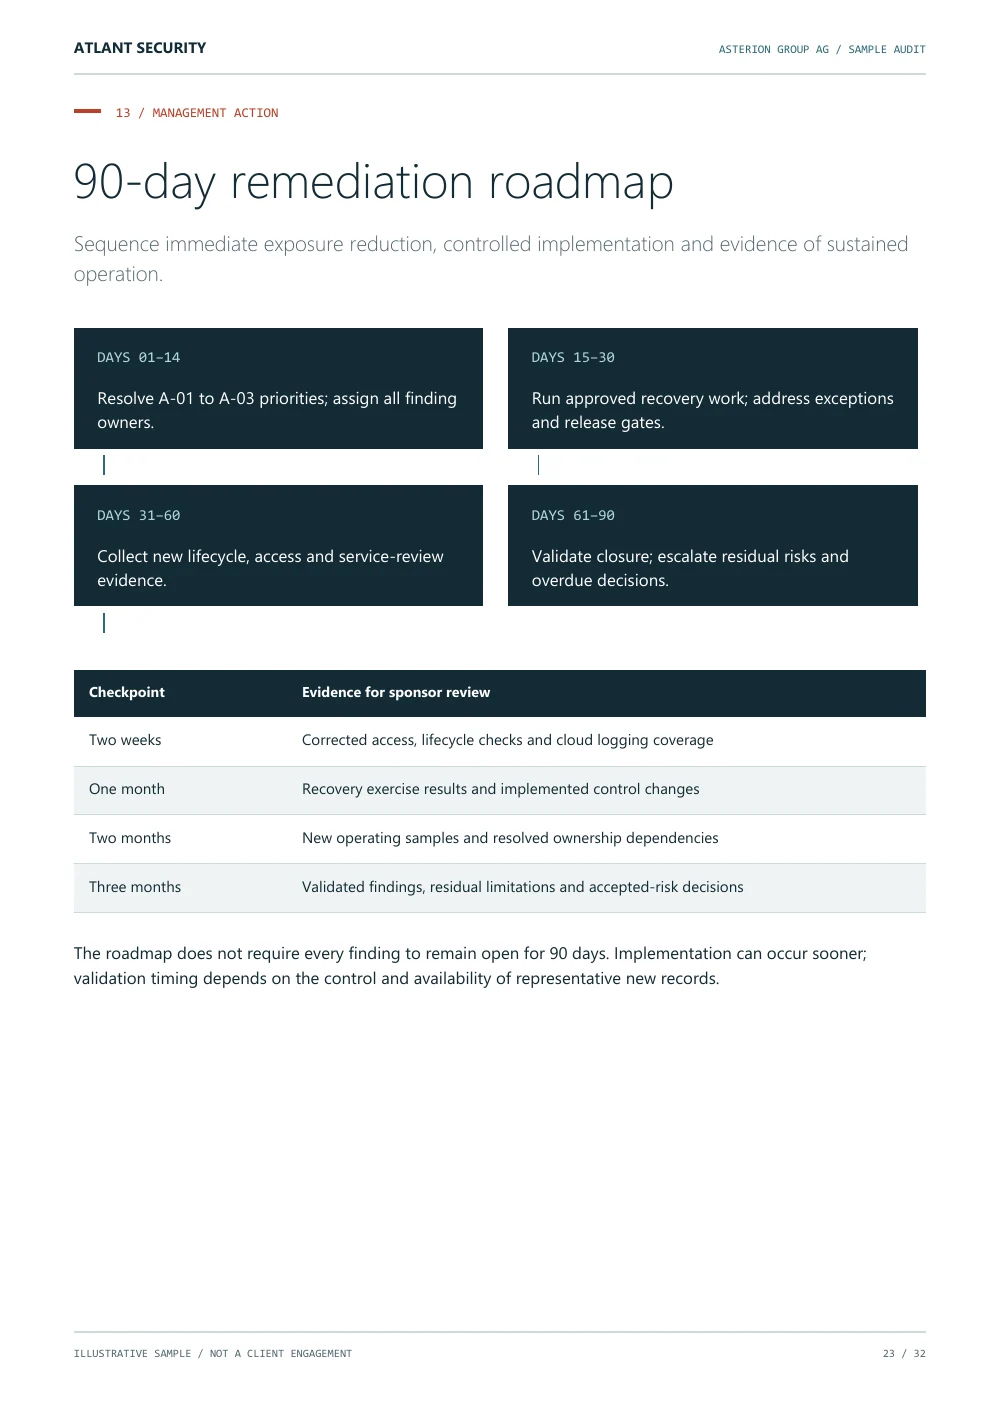
The roadmap sequences immediate corrections, controlled recovery work, new operating records and validation. A completed task is distinct from a validated finding.
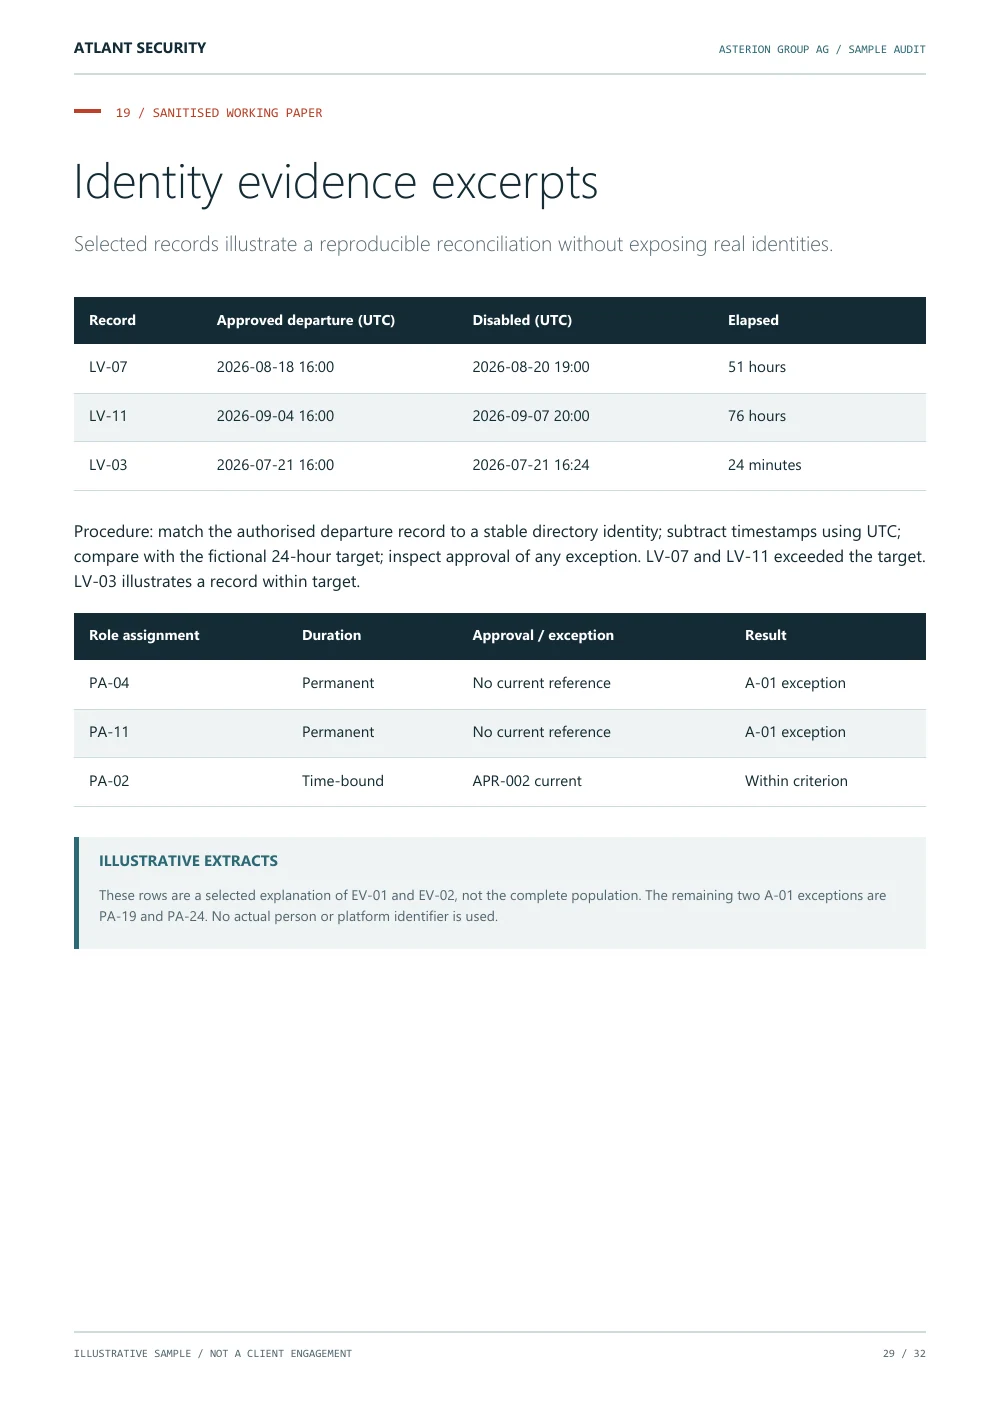
Sanitised example records show two disablement delays of 51 and 76 hours against a fictional 24-hour requirement, plus selected privileged assignment records.
END OF THE PREVIEW
Get all ten findings, the evidence register, management response, limitations and closure protocol.
Get the complete sampleSelected page images and summaries are public. The full PDF is available after the form below.
BUILT FOR CRITICAL REVIEW
Criteria, review period, populations, sample selection and documented limits.
Identity timestamps, privileged assignments, cloud configuration and release approval records.
Risk rationale, recommendations, accountable owners and explicit closure conditions.
A 90-day roadmap, responsibility model and example management response.
YOUR COPY OF THE SAMPLE
Use the example to discuss the evidence, reporting and follow-up you need.
Free PDF. Available immediately after submitting.
No newsletter subscription.
Tell us where to direct any follow-up about your request.
Your download access lasts for 15 minutes in this browser.
Download the 32-page PDFFictional organisation and assessment. Original sample by Atlant Security.
Need an alternative format? Contact our team.
No. Asterion Group AG and every record, finding and response are fictional. The report demonstrates assessment and reporting methods.
No. It demonstrates control and evidence assessment. Active technical testing requires its own authorised scope and procedures.
A scoped control assessment does not itself provide certification, statutory assurance or a universal compliance opinion. Confirm the precise requirement before commissioning work.
Yes. Upload your NDA or RFP in the contact form or the final brief step. Documents go to the team for human review and are not sent to AI.